SOC 2 Access Control Installation
Design and installation of DMP electronic access control systems supporting your physical security policies, restricted-area permissions, access monitoring and implementation documentation.
Enterprise Facilities · Audit Readiness
SOC 2 access control and physical security for technology firms and data centers. DMP systems, Turing AI video and documentation supporting audit readiness.
Technology & SaaS · Data centers · Financial institutions · Enterprise
Altora Security
Altora provides physical security systems and implementation documentation that may support a customer’s SOC 2 controls and audit readiness. Altora is not presented as SOC 2 certified, SOC 2 audited or an accredited SOC 2 auditor. Final control selection, operation, evidence evaluation and attestation remain the responsibility of the customer and its independent CPA auditor.
Two ways to engage
Design and installation of DMP electronic access control systems supporting your physical security policies, restricted-area permissions, access monitoring and implementation documentation.
Facility security assessment, access control design, installation, configuration, testing, implementation documentation and ongoing maintenance. Coordinate scope with your IT, cybersecurity and SOC 2 audit teams; this is not a CPA attestation or assurance engagement.
DMP Security · Turing AI Video
Individual employee credentials, commercial door controllers, restricted-area permissions and centralized access management for offices, data centers and enterprise facilities.
Access history, door events and reporting workflows can support auditor requests. Entry and exit evidence depends on reader placement and configuration; an uncontrolled exit does not automatically identify who left.
Configure permissions by approved job responsibilities, credential activation and timely deactivation. Support customer onboarding, offboarding and periodic access reviews without assuming an automatic HR integration.
Controlled visitor entry, temporary credentials and access event records coordinated with your visitor registration, escort and activity tracking procedures.
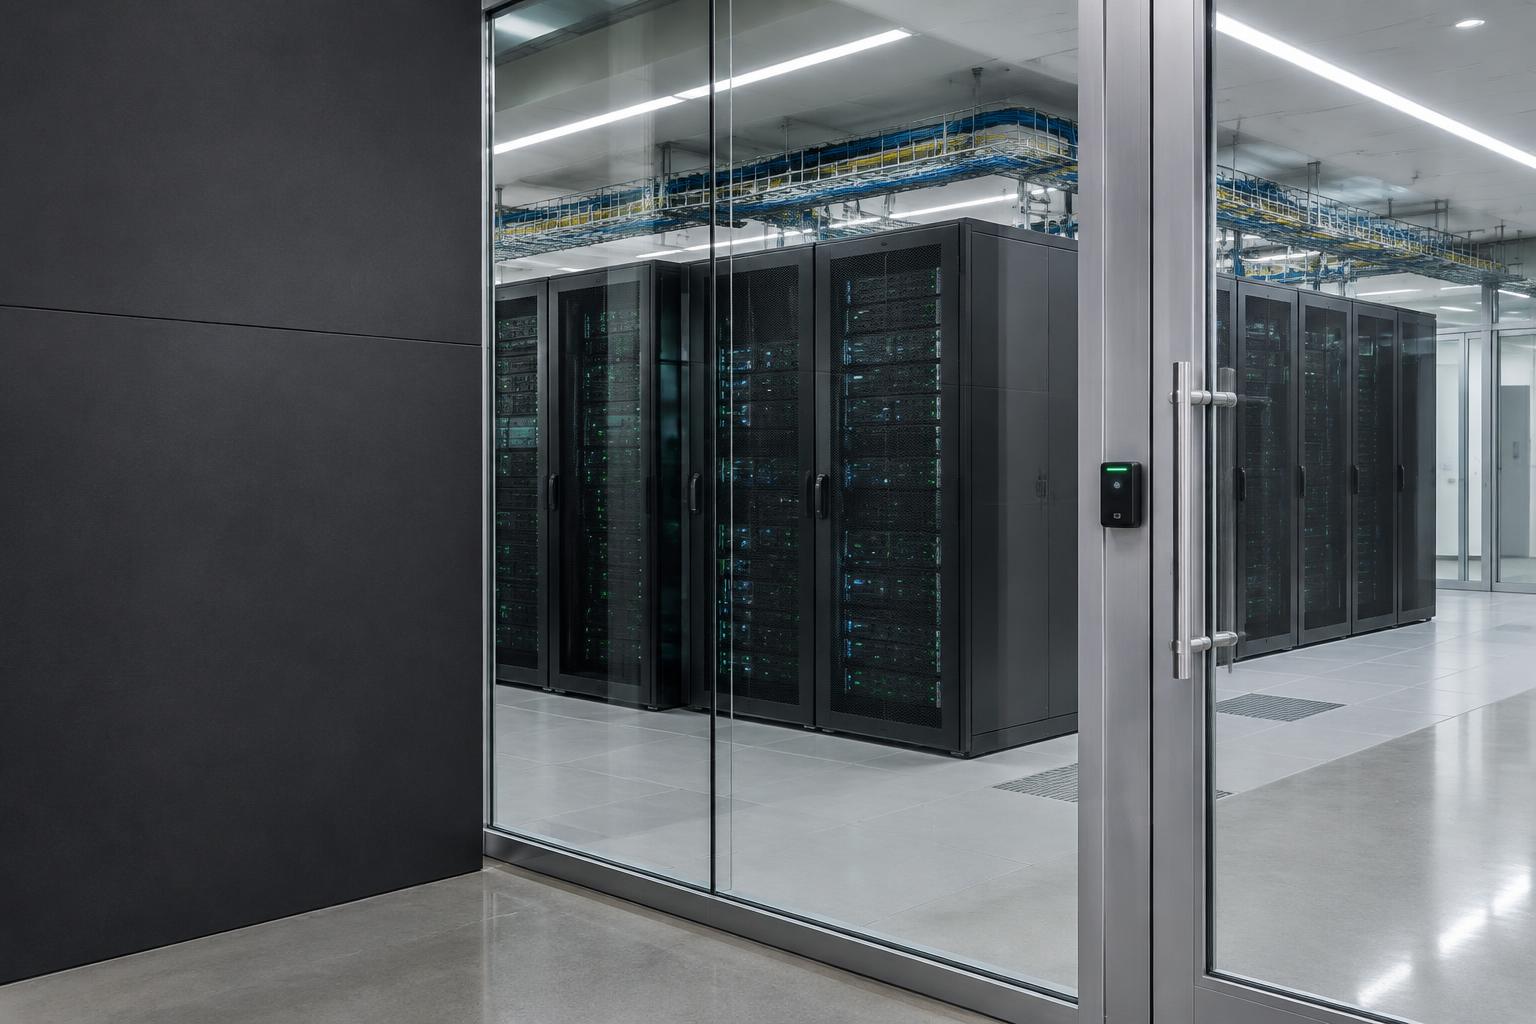
Access control for server rooms, data centers, network closets, offices and sensitive operational spaces, with door hardware and safe egress assessed for each location.
Commercial cameras, entrance monitoring, protected recording and authorized viewing. Retention, account permissions and network access are agreed with your security and IT teams.
Commercial intrusion alarms, unauthorized-entry detection and alarm notifications, coordinated with facility schedules, operator responsibilities and escalation procedures.
System inspections, access control maintenance, equipment upgrades, commissioning checks and technical support to keep the agreed physical security controls operating.
Altora implements physical security capabilities that can support relevant Trust Services Criteria. SOC 2 is an independent attestation process, not a product certification, and does not mandate a specific access control manufacturer.
Individual credentials, configured restrictions and event history can help demonstrate how physical access controls are implemented. Your organization must operate and review those controls; the independent CPA auditor evaluates evidence and determines its sufficiency.
Altora starts with your facility boundaries, sensitive rooms, operating policies and audit goals, then engineers the DMP access control and intrusion installation with Turing AI surveillance where appropriate.
Practical answers
No. DMP equipment can support selected physical security controls, but effective policies, operation, access reviews and evidence are also required. Final control selection and attestation remain with the customer and its independent CPA auditor.
No. SOC 2 is an independent attestation process based on applicable Trust Services Criteria and the organization’s controls. Altora uses DMP as its primary access control and intrusion platform for these projects; the brand itself does not establish audit readiness.
No. Altora’s service is physical security assessment, design, installation and implementation documentation. It is not a SOC 2 audit or independent CPA attestation, and Altora makes no SOC 2 certified or audited status claim.
Only if the installed readers, door configuration and reporting support that evidence. Entry-only readers, free egress and tailgating can limit attribution. Altora scopes reporting needs with your team rather than promising a complete occupancy or identity record.
Yes. Altora configures credential and permission workflows, temporary access and relevant event reporting. The customer approves access, manages visitor procedures and ensures prompt credential revocation; integrations are evaluated separately.
Provide the general site location, door and restricted-area counts, existing systems, reporting goals and timeline. Detailed audit material, access lists, passwords and sensitive facility plans should be shared only through an approved private channel.
Commercial Project Inquiry
Facility location, organization type, door/server-room count, existing access control, reporting needs and preferred assessment timeline. Do not submit passwords, personal access lists or confidential audit material.
Altora confirms project scope, site requirements and scheduling after review. An inquiry does not confirm an assessment date or any compliance outcome.
Authorized DMP Dealer